Documentation · Multi-machine
Multi-machine Cloudflare Tunnel setup
The Devices workspace (Cmd+4) lets Oh.app on your Mac inspect and steer sessions running on Linux workstations or headless Mac servers over Cloudflare Tunnel.
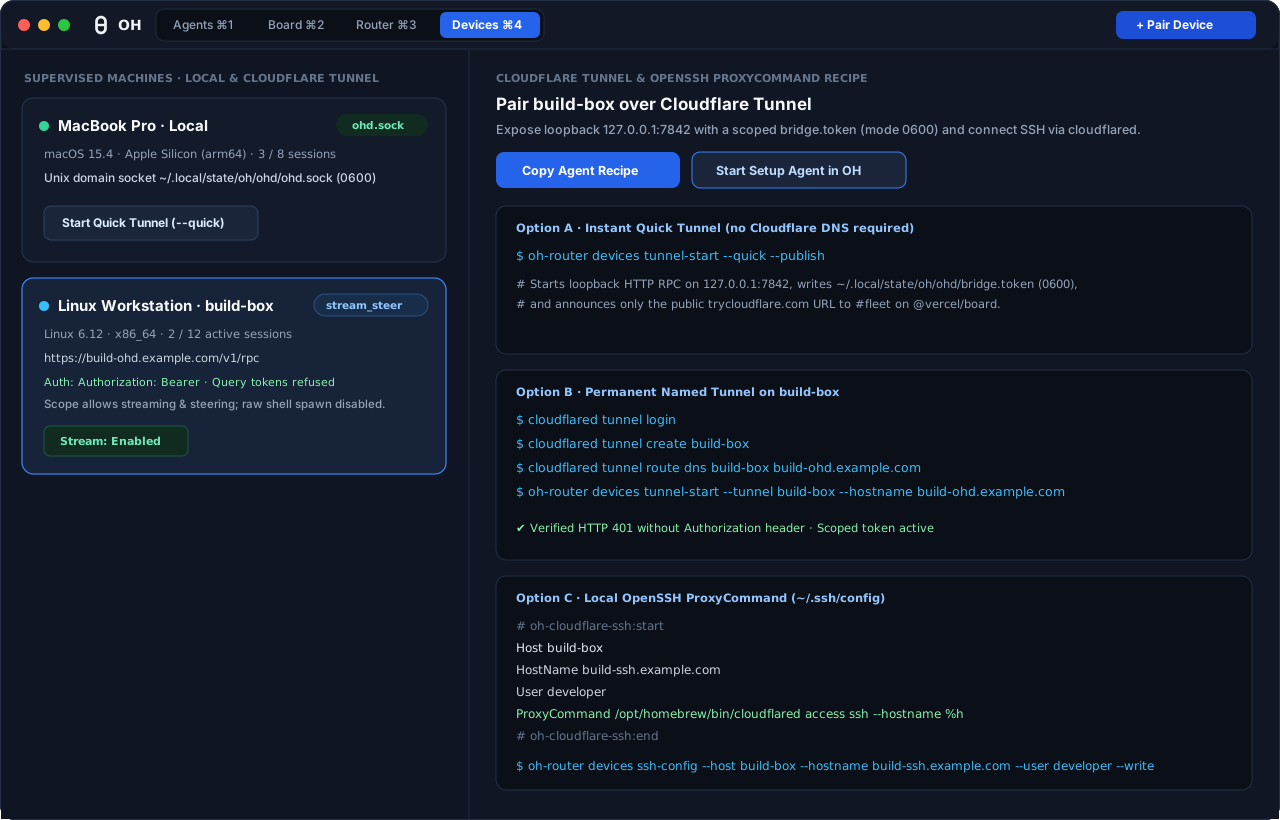
Devices workspace (Cmd+4) pairs Mac and Linux hosts over Cloudflare Tunnel with scoped stream_steer headers.Copy the multi-machine agent setup recipe
Give this setup brief to a coding agent in OH (or click Start Setup Agent in OH inside Cmd+4 Devices) to configure both the scoped HTTPS RPC bridge and OpenSSH ProxyCommand access:
Quick Tunnel and permanent Named Tunnel
ohd binds its optional HTTP RPC listener strictly to loopback (127.0.0.1:7842) and writes a random 256-bit stream_steer token to ~/.local/state/oh/ohd/bridge.token (mode 0600). cloudflared forwards HTTPS traffic to that loopback port.
Option A: start an instant trycloudflare.com Quick Tunnel with no Cloudflare DNS setup. Passing --publish announces only the public HTTPS URL (never the bearer token) to #fleet.
$ oh-router devices tunnel-start --quick --publishOption B: create a permanent Named Tunnel in your Cloudflare account and route a DNS hostname to it.
$ cloudflared tunnel login
$ cloudflared tunnel create build-box
$ cloudflared tunnel route dns build-box build-ohd.example.com
$ oh-router devices tunnel-start --tunnel build-box --hostname build-ohd.example.com
Register the remote machine on your Mac or launch Oh.app pointed at its HTTPS bridge:
$ oh-router devices add-remote --name build-box --platform linux --tunnel-url https://build-ohd.example.com --bearer-token "$OH_BRIDGE_TOKEN"Bearer tokens are accepted only in the HTTP Authorization: Bearer <token> header. Both Oh.app and ohd reject URLs that place tokens in a query string, and stream_steer scope never permits raw shell creation or profile auth changes.
Managed OpenSSH ProxyCommand block
oh-router devices ssh-config generates an idempotent # oh-cloudflare-ssh:start / # oh-cloudflare-ssh:end block for ~/.ssh/config so ssh build-box tunnels cleanly through cloudflared access ssh:
$ oh-router devices ssh-config --host build-box --hostname build-ssh.example.com --user developer --write